Applying Linear Discriminant Analysis during the data cleaning phase ensures that critical signals of potential attacks are amplified while redundant features are suppressed for faster convergence. This methodological shift is paramount as modern electrical grids transition from simple mechanical infrastructures into complex cyber-physical systems. This evolution incorporates a wide array of digital tools, including Supervisory Control and Data Acquisition (SCADA) systems and Internet of Things (IoT) sensors, to optimize energy distribution. While these advancements improve grid resilience, they also expand the attack surface, exposing critical infrastructure to sophisticated digital threats that were previously nonexistent in isolated analog environments. Standard cybersecurity protocols designed for corporate IT environments often fall short when applied to the operational technology of a power grid. Traditional firewalls and signature-based detection systems struggle to identify novel zero-day exploits or coordinated, multi-stage attacks. Furthermore, the high-stakes nature of power distribution requires near-instantaneous processing; any delay or influx of false alarms can hinder a dispatcher’s ability to prevent cascading failures. Consequently, a more integrated, proactive approach utilizing big data analytics is necessary to maintain stability across the interconnected energy landscape of the present day.
Architectural Design of the Monitoring Framework
The Three-Tier Logic: Structuring Complex Data
The proposed security framework utilizes a scalable, three-tier architecture designed specifically to manage the massive influx of telemetry data generated by grid hardware. This structure begins with a robust data layer that employs distributed agents and messaging middleware, such as Apache Kafka, to ensure reliable ingestion even during traffic spikes. By buffering raw records from system logs, network sensors, and web crawlers, the system maintains a steady flow of information into the analytical pipeline without overwhelming downstream resources. This layer acts as the foundation of the entire operation, handling the volume and velocity of big data by organizing disparate data points into standardized twelve-element tuples. These tuples include essential metadata like timestamps, IP addresses, port numbers, and protocol types, which are necessary for maintaining a chronological and contextual history of network activity. This standardized format allows the system to remain agnostic to the specific hardware manufacturer, providing a unified view of the entire power grid’s digital footprint regardless of whether the components are legacy devices or state-of-the-art IoT sensors.
High-Velocity DatProcessing and Visualization
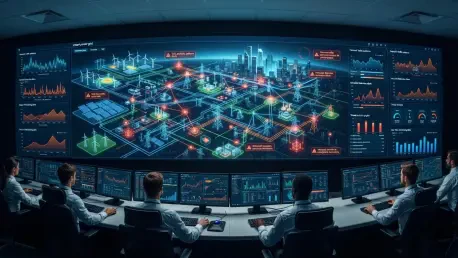
At the center of this architecture sits the function layer, which leverages the Apache Spark ecosystem to perform both real-time streaming analytics and deep offline batch modeling. This dual-processing capability is housed within a Hadoop Distributed File System, allowing for the immediate detection of ongoing threats while simultaneously refining long-term behavioral models through historical analysis. The real-time component ensures that any deviation from normal operational parameters is flagged within milliseconds, while the batch processing component allows for the retraining of machine learning models to adapt to new attack patterns. Finally, an interface layer translates these complex mathematical outputs into intuitive visual data, allowing human operators to make informed decisions during critical security events. This dispatch-centric visualization moves beyond simple alert logs, providing a holistic dashboard that illustrates the current security state of the grid. By bridging the gap between raw data and human decision-making, the interface layer ensures that technical alerts are converted into actionable intelligence that power dispatchers can use to reroute power or isolate compromised nodes before damage occurs.
Data Refinement and Preprocessing Techniques
Dimensionality Reduction: Techniques for Noise Elimination
Raw network telemetry is inherently noisy, often containing redundant data points that can degrade the performance of machine learning algorithms. To mitigate this, the framework implements Gaussian kernel density estimation to filter out outliers and group data into manageable micro-clusters. This initial cleaning phase ensures that the computational resources are focused on high-quality information rather than repetitive or irrelevant background noise that often clogs high-speed monitoring channels. By calculating the density of these clusters using Euclidean distances, the algorithm can identify and remove outliers without the massive computational overhead usually associated with continuous density calculations. This efficiency is critical in a power system where every millisecond counts and the volume of data can surge during an active cyberattack or a physical grid disturbance. The result is a refined dataset that accurately reflects the operational reality of the grid, providing a clear foundation for more complex analytical stages that follow. This systematic approach to noise reduction prevents the standard errors that often plague less sophisticated intrusion detection systems when faced with the raw entropy of modern network traffic.
Strategic Amplification: Maximizing Signal Separability
Following the initial cleaning process, the system applies Linear Discriminant Analysis to further refine the data by reducing its dimensionality. While Gaussian filtering handles noise, this step focuses on the structural complexity of the telemetry, projecting high-dimensional datasets into a lower-dimensional space where the separability between normal operations and potential attack signatures is maximized. This step is crucial because modern grid sensors generate hundreds of different features for every packet, many of which are mathematically correlated and provide no new information for threat detection. By distilling these features into their most discriminative components, the system allows the deep learning model to focus on the signals that truly matter. This refinement process significantly accelerates the convergence of subsequent neural networks, ensuring that the system can identify threats with high precision and minimal latency. In the current climate of 2026, where cyber threats have become increasingly stealthy, this ability to amplify the signal of an attack while suppressing the noise of routine grid maintenance is what separates proactive defense from reactive failure. The streamlined data allows for faster training cycles and more agile updates to the overall security posture.
Advanced Threat Classification and Correlation
Knowledge Maps: Unmasking Complex Attack Chains
To uncover subtle, multi-stage intrusions that might appear harmless when viewed in isolation, the framework utilizes a knowledge-map feature extraction module. This module treats individual security events as interconnected nodes within a graphical relationship, allowing the system to analyze the context of network activity rather than just the packets themselves. By calculating an attack correlation index, the system can link seemingly unrelated activities—such as a series of failed login attempts followed by an unusual change in a remote terminal unit’s configuration—into a coherent lifecycle of an intrusion. This graphical approach enables operators to visualize the progression of an attack across the grid topology, exposing malicious chains that would otherwise bypass isolated sensor alerts. When the correlation index exceeds a predefined threshold, these events are automatically clustered, allowing the system to calculate the exact danger state probability for specific network nodes. This holistic view is essential for identifying Advanced Persistent Threats that often move laterally through a network over extended periods, carefully avoiding the detection thresholds of traditional, time-windowed security systems that look at events only in a vacuum.
Attention Mechanisms: Temporal Dependency Tracking
The computational engine driving this classification is an Attention-based Deep Gated Recurrent Unit neural network, which is uniquely suited for the temporal nature of grid telemetry. Unlike standard feed-forward networks, this architecture is designed to track temporal dependencies and sequences of events over time, using reset and update gates to manage memory efficiently. This capability allows the system to recognize patterns that unfold over minutes or even hours, which is critical for detecting slow-moving cyberattacks that attempt to blend in with normal usage. By incorporating an attention mechanism, the network goes a step further by assigning higher weights to the most relevant features and time steps within a sequence. This effectively filters out temporal distractions and focuses the network’s processing power on the specific indicators of compromise. The output is a classification of threats into five distinct risk levels, ranging from normal operations to highly dangerous states. This granular categorization provides dispatchers with a clear understanding of the severity of a situation, moving beyond binary safe or unsafe alerts to provide a nuanced view of the grid’s security posture.
Operational Validation and Security Metrics
Quantifying Grid Health: Holistic Risk Assessment
Beyond simple threat identification, the system provides a quantitative situation value that reflects the overall health of the network in real-time. This metric synthesizes several critical factors, including the severity of known vulnerabilities as rated by the Common Vulnerability Scoring System, the operational importance of specific assets, and real-time hardware stress levels such as CPU and memory utilization. This comprehensive calculation ensures that the security assessment is not just based on network traffic, but also on the physical state of the grid’s control systems. Assets like core SCADA servers and primary distribution routers are weighted more heavily, ensuring that a threat to central infrastructure triggers a more significant response than an issue at a peripheral sensor. Scaled from 0 to 1, this situational value provides a standardized index that allows dispatchers to move from reactive troubleshooting to a predictive defensive posture. A value below 0.2 indicates healthy functioning, while a value exceeding 0.75 signals severe potential damage, giving operators a clear, data-driven mandate to initiate emergency protocols or isolation strategies before the system reaches a point of catastrophic failure.
Empirical Validation: Resilience Against Modern Deception
Evaluations using standard benchmark datasets have confirmed the effectiveness of this integrated deep learning approach in modern environments. In comparative tests, the chosen neural architecture demonstrated superior accuracy and recall over traditional machine learning methods such as Random Forest and even more complex architectures like Transformers, which often require more computational resources than are available in real-time settings. Furthermore, the system proved exceptionally resilient against False Data Injection attacks, which are designed to trick grid dispatch algorithms by sending fraudulent sensor data. By analyzing the temporal inconsistencies through the attention mechanism and checking correlations via the knowledge map, the framework successfully distinguished between genuine sensor failures and malicious attempts to deceive the grid’s state estimation logic. Hardware testing on standard utility-grade servers showed that the entire monitoring pipeline maintained stable performance metrics, with resource consumption remaining well within manageable limits even during simulated peak traffic. These results validate that the framework is not only theoretically sound but also practically deployable within the existing technological constraints of the current energy sector.
Future Directions in Grid Security
Addressing Legacy Systems: Bridging the Digital Divide
While the current framework represents a significant advancement in situational awareness, several challenges remain regarding the integration of legacy systems into the modern digital fold. Many existing power grids still rely on proprietary SCADA protocols and older hardware that were never designed for the high-speed data streaming requirements of big data analytics. To address this, the development of lightweight protocol translation agents at the interface layer is becoming a priority. These agents serve as a bridge, converting legacy signals into the standardized twelve-element tuples required by the processing engine. This approach allows utilities to upgrade their security posture without the prohibitive cost of replacing every physical component in the grid. Furthermore, the transition toward 2027 and beyond will require a move away from static datasets for training, as attackers constantly evolve their tactics to bypass known defenses. Future iterations of this system will likely incorporate continuous learning loops where real-world data from the interface layer is used to periodically retrain the models, ensuring that the detection logic remains relevant against the next generation of sophisticated botnet activities.
Strategic Evolution: Game Theory and Immutable Ledgers
Looking forward, research has shifted toward integrating mixed-strategy game theory to better model the interactive tactical match between attackers and defenders within the grid. This approach allowed for the calculation of defensive rewards and the optimization of resource allocation during an active incident, providing a mathematical basis for automated response. There was also significant potential identified in the exploration of blockchain technology to create a verifiable, immutable ledger for all telemetry data. By ensuring that the data analyzed by neural networks remained untampered with at the source, these enhancements hardened the grid against adversaries attempting to manipulate the security system itself. Ultimately, the transition to this deep-learning-driven situational awareness model provided a necessary blueprint for the survival of critical infrastructure. The combination of high-speed data cleaning and attention-based classification transformed the way grid operators perceived digital risk. By establishing a proactive rather than reactive stance, the framework secured the foundations of the smart power system, ensuring that energy distribution remained resilient in the face of increasingly complex global cyber threats. This shift in strategy successfully bridged the gap between operational technology and advanced cybersecurity.